Madsalt Supabase Checker
Connect a Supabase project read-only and get a graded security report, with fixes you can paste into your coding agent.
 MS
Project links
Visit productRequest correctionProject Note
A closer look at Madsalt Supabase Checker
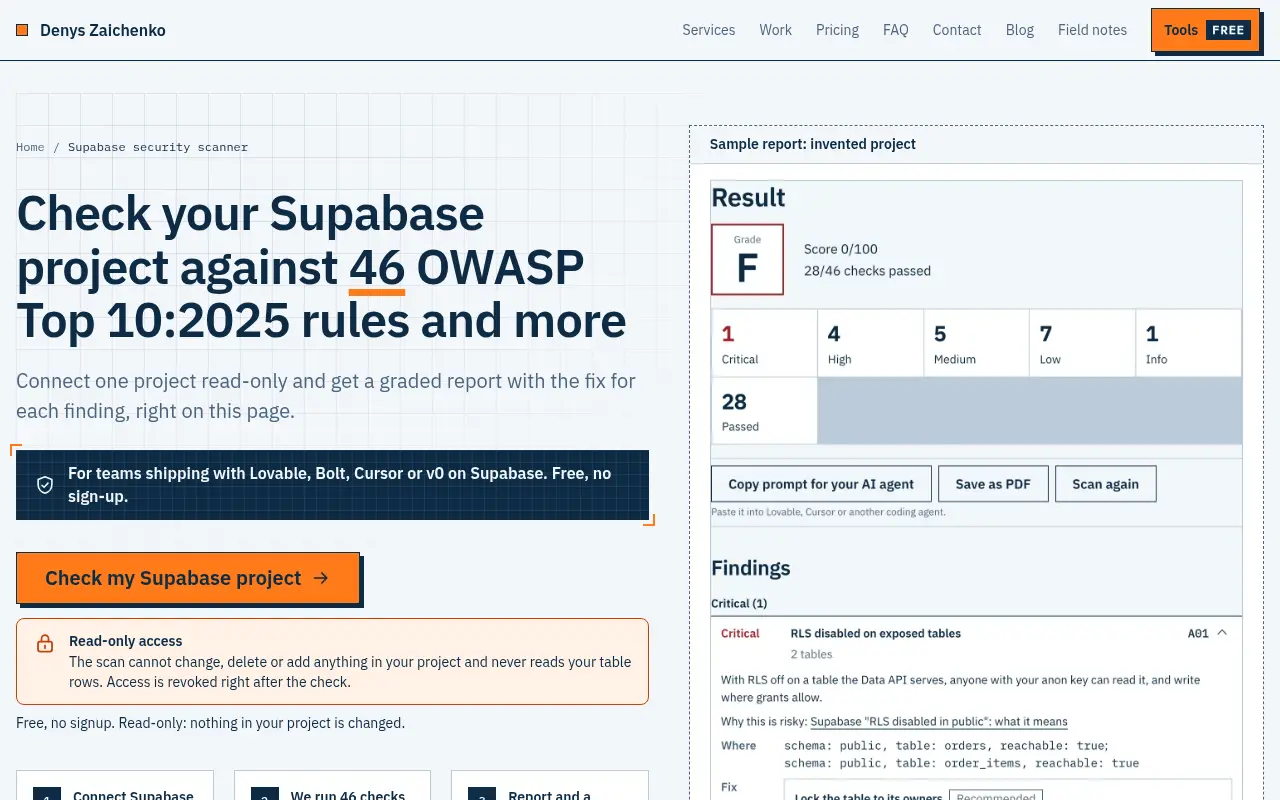
A free, read-only scanner that checks a Supabase project against 46 security rules and gives a fix for each finding.
The app works. Is the database open?
You built an app over a weekend with an AI coding tool. Sign-up works, the dashboard loads, and a friend has already made an account. What you can't see from the browser is whether a stranger holding your public key could read every row in a table, because row-level security was never switched on.
That's the worry this free scanner is built for. Its page is aimed at teams shipping with Lovable, Bolt, Cursor or v0 on Supabase. You connect one project read-only, and it checks that project against 46 rules mapped to the OWASP Top 10:2025.
What it reads, and what it leaves alone
Connecting means approving read-only access through Supabase's own login. You then pick a project, confirm you're human and start the scan. The checks cover access and row-level security, sign-in settings, storage, Edge Functions and infrastructure.
To do that, the scanner reads the database catalog, which holds things like tables, policies and grants. It also reads auth settings such as password rules and MFA, the list of storage buckets, and project settings such as backups and SSL. The page is just as specific about what it never reads. Rows in your tables, files in your buckets and your app code are all off limits, and any API key that turns up in a settings reply is dropped without being stored. The access grant is revoked right after the check.
The result is a graded report with a fix for each finding, given as SQL or a dashboard setting. There's also a prompt you can paste into Cursor, Claude Code or Lovable, which is a nice touch for people who built the app that way in the first place.
Free, with a consultant behind it
The check is free and needs no sign-up beyond the Supabase login. A report is stored only if you create a share link, and then for seven days at most. According to the privacy page, last updated November 5, 2026, the access token sits in a sealed cookie that expires 15 minutes after you connect.
The page is frank about its blind spots. Two of the ten OWASP categories are marked as not checkable, because insecure design and error handling live in app code. It also can't tell whether one signed-in user can read another user's rows, which needs a test with two real accounts. A clean report doesn't mean a safe app.
The site is run by Denys Zaichenko in Porto, Portugal, and it doubles as his shop window. The same menu and footer link to his paid services, including an app audit listed at €490. The checker is useful by itself, and it also introduces someone who'd fix the findings for a fee.
If you shipped on Supabase in a hurry, a scan is a sensible way to find out what you left open.
Project note details
Dates and editorial links
Published
November 12, 2026
Updated
November 12, 2026
Note history
Publication and substantive update dates for this public note.
- Nov 12, 2026
- Project note published.
Want to come back to Madsalt Supabase Checker?
Save it to this browser. Your Saved list marks projects whose note or updates changed since you last looked.
Keep exploring
More like Madsalt Supabase Checker
- Remote Jobs Scraper (TinyRex)Developer Tools · An Apify actor that pulls remote job listings from six boards through their official APIs and feeds, priced at $0.80 per 1,000 jobs.
- Agent-Ready Repo AuditorDeveloper Tools · Checks public GitHub repositories for agent instructions, issue intake, and verification commands, then turns the findings into a report.
- AI CheckerAI & Skills · AI Checker is a Japanese-language tool that reviews a passage of 100 to 10,000 characters and gives a reference score with reasons.
- PerchDeveloper Tools · An open-source CLI and pull request check that applies plain-English code rules and model-based bug and security scans to each changed method.
- Public Issue Evidence CapsuleDeveloper Tools · A read-only GitHub Action that records a bounded evidence packet for one public, non-security issue.
- AssaySaaS · Company research for outbound teams where every field carries the sentence it came from, and a second check flags any quote that doesn't back the claim.
- EveryPay for JoomShopping by InteroperiaDeveloper Tools · A payment plugin that adds EveryPay to JoomShopping stores and checks each result against the order.
- Metric OwlDeveloper Tools · Metric Owl is an open-source, self-hosted Linux server monitoring tool with a live dashboard, local alert rules, email alerts, optional AI chat with your own key and read-only MCP.
For the makerAdd the badge to your site
If you made Madsalt Supabase Checker, you can post about this note with a ready-to-edit announcement, or show it on your own site with an optional badge that links back here. Neither changes the note's text or placement. This note's link to the project is marked as user-submitted until the project's site links back, for example with the badge, and is a standard link while it does.

Want to keep this note's facts current yourself? Project Radar Pro lets a verified maker confirm status, pricing and platforms in a labeled block, post one update a month and see the note's activity totals. It never changes the note's text or placement. See what Pro includes
Building something useful?
Submit your project for free. If selected, it gets a Project Note that explains what it does and links to your work. Publication isn't guaranteed.
Submit a project